Journal entry control deficiency remediation in six steps:
- Classify the deficiency (design or operating; deficiency, significant deficiency or material weakness)
- Confirm the root cause and scope
- Put interim compensating controls in place
- Redesign the control
- Operate and test the redesigned control
- Assemble evidence for the auditor’s retest
Common Journal Entry Control Deficiencies Auditors Flag
- Approval missing, or evidenced only after the journal posted
- The same person prepared and approved the journal, breaking segregation of duties
- Posting access wider than the user’s role requires
- Review sign-offs with no record of what the reviewer checked
- Supporting documentation missing or stored away from the journal
- Journals posted outside the reviewed process, leaving the reviewed population incomplete
Design Deficiency vs Operating Deficiency: Which One Is It?
- Design deficiency: A necessary control is missing, or an existing control would not meet its objective even if performed as designed.
- Operating deficiency: A properly designed control does not operate as intended, or the person performing it lacks the necessary authority or competence.
Significant Deficiency vs Material Weakness: How Is the Finding Classified?
PCAOB AS 2201 distinguishes between control deficiencies, significant deficiencies and material weaknesses according to their severity. Appendix A, paragraphs .A3, .A7 and .A11, provides the relevant definitions.
| Classification | Definition (paraphrased from AS 2201) | Who is informed |
|---|---|---|
| Other control deficiency (less severe) | The design or operation of a control does not allow misstatements to be prevented or detected on a timely basis | Management, in writing under the integrated-audit communication requirements |
| Significant deficiency | Less severe than a material weakness, yet important enough to merit the attention of those overseeing financial reporting | Audit committee, in writing |
| Material weakness | A reasonable possibility that a material misstatement of the annual or interim financial statements will not be prevented or detected on a timely basis | Management and audit committee, in writing; management cannot conclude ICFR is effective, and public disclosure is required for applicable SEC registrants |
- Fraud on the part of senior management, whether or not material
- Restatement of previously issued financial statements to correct a material misstatement
- A material misstatement found by the auditor that the company’s controls would not have detected
- Ineffective audit committee oversight of external financial reporting and ICFR
When does a journal entry control weakness become a reportable deficiency?
What Should a Journal Entry Remediation Plan Include?
- Root cause statement : Explain why the control failed, distinguishing between design and operation. Identify whether the underlying issue involves inadequate procedures, unclear ownership, insufficient competence, ineffective supervision or inappropriate system access.
- Scope : Define the journal types, entities, users and periods affected. Consider whether similar controls elsewhere in the organisation share the same weakness, and whether earlier reporting periods require further investigation.
- Redesigned control : Set out the control owner, how often the control runs, the precision of any review and the evidence the control produces each time it operates. The redesign should directly address the identified cause.
- Interim measures : Document the temporary controls that will manage the identified risk while the redesign is implemented and tested. These measures should have defined responsibilities, review criteria and supporting evidence.
- Timeline and test points : Establish the implementation date, the period needed to demonstrate operation and the planned management testing. Discuss the expected audit evidence and testing approach with the external auditor while retaining management responsibility for the design and implementation.
- Governance : Name an accountable owner, define how remediation progress and unresolved risks will be reported to the appropriate management and oversight bodies, and maintain the disclosures required for any reported material weakness.
Which Interim Compensating Controls Work During Remediation?
- Defined precision: The review must specify what is examined, which exceptions require investigation and the criteria used to determine whether further action is necessary.
- Complete and accurate information: The journal population or report used in the review must be sufficiently reliable for the control’s purpose.
- Evidence of the review: Records should show what the reviewer examined, which exceptions were investigated, the conclusions reached and any corrective action taken.
- Independent retrospective review of posted manual journals above a defined threshold or meeting specified risk criteria
- Temporary restriction of posting access to a smaller group of authorised users
- Targeted review of journals posted by users with elevated access
The effectiveness of these measures depends on their scope, frequency and precision. For example, a review limited to high-value journals may not address a weakness involving repeated lower-value postings or inappropriate user access.
These additional reviews may increase the workload during period-end close. Their scope and effectiveness should be reassessed as permanent controls are introduced.
How to Redesign Journal Controls So the Fix Holds
The following table illustrates how different remediation approaches may address common journal control deficiencies.
| Remediation need | Manual redesign | System-enforced redesign |
|---|---|---|
| Approval before posting | Documented independent sign-off before posting | Workflow configured to block posting until the required approvals are complete |
| Segregation of duties | Defined role separation and periodic access monitoring | Requester-versus-approver separation enforced according to the configured approval policy |
| Posting access | Access reviews and documented restrictions | Direct posting access restricted through appropriate SAP roles and, where applicable, service-user configuration |
| Supporting documentation | Controlled document storage with journal references | Attachments held with the journal |
| Population completeness | Reconciliation and exception review | Defined journals routed through the controlled process, with access restrictions and checks for bypassed entries |
These approaches are illustrative, and their effectiveness depends on the organisation’s control environment.
How Promenta Supports System-Enforced Journal Controls in SAP
Its configurable workflow supports approval routing based on journal attributes such as company code, journal value and G/L account, allowing organisations to define approval paths according to their financial-control requirements.
Where independent approval is required, the workflow can enforce requester-versus-approver separation. Approval thresholds and any permitted exceptions are determined by the organisation’s configured approval rules.
What Evidence Will the Auditor Expect at Retest?
Following implementation, management should assemble evidence demonstrating the redesigned control’s effectiveness against the original deficiency.
- An updated control narrative and risk and control matrix
- Walkthrough evidence showing the redesigned control in operation
- Management’s own operating-effectiveness testing, with samples and results
- A complete listing of journals for the post-remediation testing period, reconciled to the general ledger
- For each sampled journal: preparer, approver, timestamps, supporting documentation and proof that approval preceded posting
- Current listings of users able to post journals, including relevant privileged access
- For configured controls: evidence of the configuration and of any changes made to it
How Long Does It Take to Remediate a Journal Entry Control Deficiency?
- Control frequency : A monthly close review produces far fewer instances to test than a daily control. The required operating period must allow sufficient evidence to be gathered for the relevant control.
- Scale of the redesign : A revised review procedure may be implemented relatively quickly, while changes involving system configuration, access controls, training or additional procedures can require more time.
- Go-live timing : A control launched late in the year may not operate often enough before the assessment date to support a conclusion on operating effectiveness.
Conclusion
Prepare → Validate → Submit → Route → Review → Approve → Post → Audit
Promenta’s SAP Journal Entry Management solution provides configurable validation, approval and audit capabilities that can support this process within SAP</s
Frequently Asked Questions
1. What is a journal entry control deficiency?
2. What does an auditor typically flag in a manual journal entry population?
3 . What is the difference between a control deficiency, a significant deficiency and a material weakness?
4. What does a credible journal entry remediation plan contain?
5. Does correcting the sampled journals fix the deficiency?
Journal Entry Solution for SAP: What Finance Teams Should Evaluate
A journal entry solution for SAP is a structured process and technology layer that governs how manual general ledger entries are prepared, validated, approved, posted and evidenced within SAP ECC or S/4HANA. Unlike simple upload tools, a governed solution connects preparation, approval controls, segregation of duties, and audit trail into one continuous process inside SAP.
Posting is often where weaknesses earlier in the journal process become visible.
A journal may fail validation late in the close. An entry may be prepared for the wrong period. Approval evidence may sit in a mailbox rather than alongside the finance document. Or finance teams and auditors may need to reconstruct who reviewed an entry several months after it was posted.
The issue is not necessarily how the journal was prepared.
Excel remains a familiar and effective tool for calculations, analysis and complex journal preparation. The greater control question is what happens around that preparation: how the journal is validated, who approves it, how segregation of duties is enforced, when it reaches SAP and where the supporting evidence is retained.
In many organisations, these activities have developed separately over time. Excel supports preparation, email supports approval, spreadsheets track progress and SAP is used for the final posting.
Each component may work.
The weakness appears in the handoffs between them.
This matters as the wider compliance environment becomes more complex.
The 2025 KPMG SOX survey of roughly 150 SOX professionals found the average number of in-scope systems increased from 17 to 40 in two years, while automated controls fell from 21% to 17% of the control population.[1]
More systems inside audit scope, proportionally fewer controls running by rule. This means finance teams are managing more systems with proportionally fewer automated controls – exactly the environment where a structured journal entry solution for SAP becomes a compliance necessity, not a convenience.
A better journal entry management solution for SAP must address more than posting.
It should strengthen the process from preparation and validation through approval, evidence, posting and reporting.
What Most SAP Journal Workflows Actually Look Like
SAP journal entry management in most organisations has developed incrementally rather than from a single end-to-end design.
That does not mean the underlying practices are inherently wrong.
The risk arises when preparation, approval, validation, posting and evidence operate as separate activities with weak connections between them.
Validation Happens Too Late
In a fragmented process, SAP-specific issues may only become apparent when the journal reaches the posting stage.
Posting-period restrictions, incomplete fields, incorrect master data or other validation issues can therefore surface when the close timetable has the least flexibility.
An error identified during preparation is relatively straightforward to correct. The same error discovered after approval may require the journal to be amended, reviewed and approved again.
This close delay risk is largely created by the sequence, not by the people involved.
Approval Routing Depends on Individual Knowledge
Approval structures can also become dependent on precedent.
A preparer may know who normally reviews a particular type of journal because the same person approved it the previous month.
However, this does not necessarily demonstrate that the approver is appropriate for the company code, journal value, account or business area involved.
Often, it becomes difficult to demonstrate if segregation of duties has been applied consistently.
Evidence Is Fragmented
The calculation may remain in Excel.
The approval may sit in email.
The final finance document sits in SAP.
When these elements are separated, finance and internal audit teams may need to reconstruct the history of a journal from several sources.
The journal itself may be correct, but teams may struggle to show the evidence around it.
Posting Authorisations Become a Practical Workaround
Where the approval process operates outside SAP, finance users may continue to retain powerful posting transaction codes because somebody needs the ability to complete the process.
While it does not automatically create a control failure, the broader standing access can increase the importance of compensating controls and create additional segregation-of-duties considerations.
How to Tell Whether the Journal Process Is Still Heavily Manual
A useful starting point is to look at what happens during period close.
● Are approvals regularly followed up through email or chat?
● Are SAP validation errors commonly discovered after a journal has already been reviewed?
● Is a spreadsheet used to establish which journals are awaiting approval, approved or posted?
● Can finance teams produce, from one place, the preparer, approver, supporting documentation and status of a particular journal?
● Do journal preparers continue to hold powerful SAP posting authorisations because the process depends on manual posting?
One of these characteristics on its own may not indicate a significant weakness.
If several of these are true, teams must closely examine their journal workflow.
What a Journal Entry Solution for SAP Should Include
A better journal entry solution for SAP is not simply a longer list of automation features.
The sequence matters.
Ideally, the journal should be validated against SAP rules before submission, routed according to defined approval logic, supported by appropriate documentation and recorded as it progresses through the workflow.
These capabilities are strongest when they operate as one governed process.
There is also an architectural decision to consider.
An organisation can build journal workflow functionality through bespoke SAP development, use a separate platform that interfaces with SAP or implement a configured SAP-native workflow solution.
According to the organisation’s requirements, each model can provide useful capabilities.
The key questions to consider are –
● Where the journal data resides,
● Where validation takes place,
● How approval rules are maintained,
● How evidence is connected to the finance document, and
● What additional systems need to be governed.
These distinctions affect control, compliance and operational efficiency.
Built natively on SAP. No external servers, no duplicate financial data.
How a Journal Entry Solution for SAP Strengthens Control
Control does not mean adding approval steps for their own sake. Rather, it ensures the required path and standards are applied consistently.
Route Journals According to Defined Rules
Approval requirements can vary considerably.
A low-value journal may autopost, or require a relatively simple approval path. A high value journal involving a particular company code or G/L account may require additional reviewers, teams or approval levels.
A structured workflow can use information in the journal request itself to determine the appropriate route.
Promenta supports configurable routing using any field in the journal request, such as company code, journal value and G/L account, from simple one-step approval through to multi-team and multi-level processes.
So, the advantage is not simply automation; it is more about following a planned, documented and controlled process, consistently.
Enforce Segregation of Duties Within the Process
A documented segregation-of-duties policy is useful. However, a strong control is one that makes the workflow enforce it.
For example, a requester should not normally be able to approve the same journal unless the organisation has explicitly defined an exception within its approval rules.
Promenta supports this form of requester-versus-approver control and can restrict journal requests according to authorised SAP users and areas of responsibility.
This reduces reliance on individuals remembering which control applies to each transaction.
Validate Before the Journal Enters Approval
Validation is most valuable when it happens before an approver spends time reviewing the entry.
With an SAP-integrated preparation process, journal data can be checked against SAP master data and finance rules as part of preparation. A simulated posting can then identify SAP-specific posting issues before the journal is submitted for approval.
Promenta’s SAP Journal Entry Workflow supports Excel-based submission with SAP pick lists and a full posting simulation before the request can be submitted.
This changes the role of approval.
The approver is reviewing a journal that has already passed key system checks rather than one that may still fail when it reaches SAP.
Compliant and Audit-Ready Journal Posting
A robust SAP journal entry workflow solution is not measured solely by whether an approval happened.
It is also about whether the organisation can demonstrate what happened, who was involved and what evidence supported the decision – covering SOX evidence, audit trails, and segregation of duties
Capture the Audit Trail as the Journal Moves
A workflow can record the request, approval, rejection and subsequent processing of the journal as those events occur.
This is stronger than reconstructing the sequence later from email and separate trackers.
Promenta provides real-time process reporting and an audit trail of users who approved or rejected a journal request, with the information available from within SAP.
The evidence exists because the process created it.
Keep Supporting Documentation Connected
Manual journals often rely on supporting material such as calculations, schedules, or explanations.
Those documents are part of the control environment.
Where supporting evidence travels with the journal request and remains connected to the finance document, reviewers can assess the journal and its basis together. It also becomes easier for finance and audit teams to retrieve the same evidence later.
Promenta supports multiple evidence attachments that can be saved in SAP against the finance document.
Reduce Dependence on Powerful Posting Access
A governed workflow may also allow organisations to reconsider which users genuinely require direct posting access.
Promenta provides the option to remove powerful SAP Finance transaction codes from end users where the organisation’s process and control model allow it.
This is an important distinction.
Approval controls and access controls should reinforce one another.
Journal Testing Still Matters
A controlled workflow does not remove audit scrutiny of journals.
PCAOB AS 2401 requires auditors to design procedures to test the appropriateness of journal entries and other adjustments as part of the response to the risk of management override. The standard also notes that testing ordinarily focuses on entries around the end of a reporting period, while considering whether testing across the wider period is also necessary.
A better workflow therefore does not eliminate journal risk – but it does improve the manual journal entry controls in SAP that auditors test when they review the close.
It improves the quality, consistency and accessibility of the evidence available when those journals are reviewed.
Can a Journal Entry Solution for SAP Be Both Fast and Controlled?
Speed and control are sometimes treated as opposing objectives. But they don’t need to be.
Much of the avoidable delay in journal processing comes from rework, incomplete information and waiting for approvals.
Reduce Posting Rework
When a journal has been validated and subjected to posting simulation before approval, SAP-specific errors can be identified earlier.
That can reduce the likelihood of a journal reaching the end of the process only to require correction, resubmission, and another approval cycle.
The goal must be to get the journal right earlier in the process while accelerating posting.
Reduce Manual Approval Chasing
Email-based approval can become difficult when approvers are unavailable, or responsibility is unclear.
Workflow notifications, team inboxes, substitute approvers, and forwarding can help keep requests moving without bypassing the defined approval structure.
Promenta provides these workflow capabilities within its journal solution.
Teams benefit from less manual coordination, not less governance.
Manage Higher Journal Volumes Without Weakening the Process
Period close can involve large journals, recurring entries, and multiple journals that need to be processed within a limited timeframe.
SAP documentation identifies a 999-line-item constraint in a number of standard FI posting scenarios, although the technical treatment can vary by S/4HANA configuration and posting process. Promenta supports journals with more than 999 line items as well as multiple journals within a single request.
Process reporting gives controllers the visibility of what has been approved, posted, and remains outstanding.
This is where control and efficiency reinforce one another.
See a Journal Move From Excel to Posted Inside SAP
A journal entry solution for SAP processes a manual journal through eight connected stages: Prepare, Validate, Simulate, Submit, Route, Approve, Post, and Report. Each stage must be connected to the next for the control to hold. A useful evaluation is to follow one journal through the complete process:
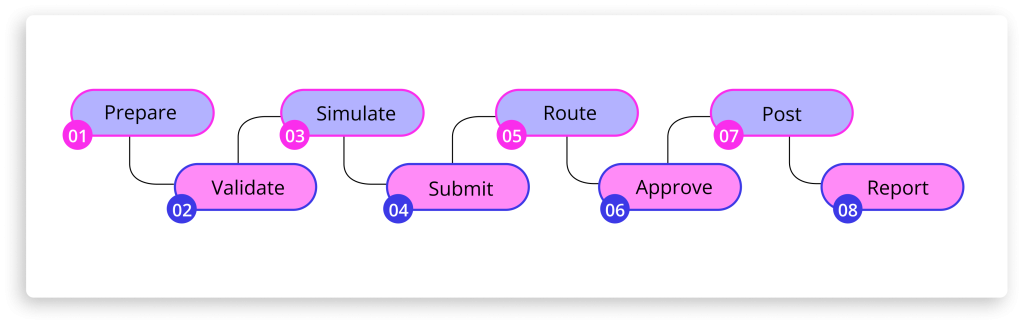
Instead of fixating on the number of individual features within the process, teams must focus on keeping each stage connected to the next.
Consistency helps enforce the right controls at the right stage.
See Promenta’s SAP Journal Entry Workflow solution
Native SAP Journal Workflow vs External Solutions: Key Differences
When evaluating a journal entry solution for SAP, organisations typically choose between three models: native SAP-configured workflow, bespoke custom development, or an external close platform that interfaces with SAP. The right SAP journal entry management software should fit the organisation’s deployment model, control requirements and upgrade path. The table below compares a configured SAP-native journal workflow with bespoke or external workflow approaches across key governance dimensions.
Some organisations develop functionality inside SAP. Others use external close or workflow platforms. Others prefer a configured SAP-native solution.
The most appropriate approach depends on the organisation’s SAP landscape, wider finance architecture, control requirements and existing technology investments.
| Dimension | SAP-Native Journal Entry Solution | Bespoke or external workflow |
| Approval rules | Can be maintained through configured workflow logic, depending on the solution | May be maintained through custom development or on a separate platform |
| Validation point | Can validate directly against SAP finance rules before submission | Depends on the design and integration; some SAP-specific validation may rely on interfaces or occur later |
| Finance data during approval | Remains within the SAP environment | May be processed or stored on an additional platform |
| Evidence and attachments | Remains connected to the SAP workflow and finance document | May reside across the workflow platform, SAP and other repositories |
| Governance scope | Keeps workflow and evidence within the existing SAP control environment | Introduces additional applications, interfaces or connectors for IT and control teams to consider |
| Ownership | Product configuration and maintenance can remain vendor-supported | Bespoke developments require internal ownership or ongoing implementation support |
| Upgrade considerations | SAP-certified products can reduce some compatibility concerns, although appropriate testing is still required | Custom code and integrations may require additional regression testing or remediation during upgrades |
This architectural distinction matters because journal governance depends not only on the approval steps.
It also depends on where sensitive finance data is stored, where validation takes place, how access is controlled, and where audit evidence is retained. For a step-by-step breakdown of how approval routing works in practice, see the SAP Journal Entry Approval Workflow guide.
How Promenta’s Journal Entry Solution for SAP Works
Once the process and control requirements are clear, the technology decision becomes easier to assess.
Promenta’s SAP Journal Entry Management Workflow deploys and runs inside SAP ECC or S/4HANA and integrates with the organisation’s existing SAP finance rules, transactional validation and security model. The solution is SAP certified for ECC and S/4HANA.
Preparers can work through the browser or use the Promenta Excel Add-in.
So, Excel can remain part of journal preparation without operating outside the controlled process.
Journal requests can include supporting documentation, undergo posting simulation before submission, and follow configurable approval routing based on finance-relevant fields. Browser and SAP Fiori mobile approvals are supported, while process and audit reporting remain available from within SAP.
Promenta has specialised in SAP data process automation since 2002 and is certified by SAP as a provider of SAP solutions.
What Should Change at the Next Close?
A better journal entry solution for SAP should not require finance teams to choose between control and efficiency.
The objective is to improve both.
Early validation can reduce rework, and rule-based approval can improve consistency.
Connected evidence can strengthen audit readiness.
Better process visibility can help controllers identify outstanding journals before they become a close issue.
And Excel can continue to support journal preparation where it remains the most practical tool.
The end goal should be to support manual journals with a better control process.
Before the next period end, finance leaders may want to consider three questions.
● Can controllers see which journals are prepared, awaiting approval, approved and posted without reconciling several trackers?
● Can finance or internal audit demonstrate who prepared and approved a specific journal and retrieve its supporting evidence from a connected process?
● And if the SAP landscape changes, can the journal workflow move with it without creating an unnecessary governance and maintenance burden?
Frequently Asked Questions
What should finance teams look for in a journal entry solution for SAP?
A journal entry solution for SAP should be evaluated on where validation takes place, how approval rules reflect the organisation’s governance model, how segregation of duties is enforced, where supporting evidence is retained, and how the workflow survives SAP upgrades.
Finance teams should consider where validation takes place, whether approval rules can reflect the organisation’s governance model, how segregation of duties is enforced, where supporting evidence is retained and how the workflow is maintained through SAP changes.
Architecture should also form part of the evaluation.
A solution that requires journal data, approval records and evidence to move across several systems and outside of your network creates a different control model from one that operates natively within SAP.
Can journal posting become faster without weakening control?
Yes.
Faster posting does not necessarily require fewer controls.
Delays often occur because errors are identified late, journals need to be resubmitted or approvers need to be chased manually.
Earlier validation and structured routing can address those delays while preserving the required review and approval process.
What is the difference between a native SAP journal workflow and a non-native workflow?
A native workflow operates within the SAP environment and can use the existing SAP finance rules, validation logic, security and authorisation model.
A non-native workflow operates through an additional platform, potentially outside your network and interfaces with SAP.
That does not make an external platform inherently unsuitable. Many organisations use them successfully, particularly across mixed ERP environments.
The distinction is architectural.
Finance and SAP teams should understand where journal data and approval evidence reside, where SAP-specific validation takes place, what integrations are required and which systems form part of the governance and audit environment.
Can journals prepared in Excel still be properly controlled?
Yes.
Excel remains useful for calculations, analysis and complex journal preparation.
If the preparation process has a real-time integration with SAP master data and validation, submits the completed journal into a governed approval workflow and preserves the required supporting evidence, Excel can remain the preparation layer while the control framework continues to operate in SAP. Finance teams can also use Promenta’s free SAP journal posting Excel upload tool as an entry point to that governed process.
Does a better journal workflow reduce audit risk?
A structured journal workflow can reduce risks created by fragmented evidence, inconsistent approvals, late validation, and poorly controlled access.
It does not remove the need for audit testing or professional judgement.
PCAOB requirements continue to require journal-entry testing as part of the auditor’s response to management-override risk.
What a controlled workflow can change is the quality of the evidence available: identifiable preparers and approvers, demonstrable separation of duties, connected supporting documentation and a consistent population from which journals can be reviewed.